ubonile.co.za
 Closed pilot
Public safety platform
Ubonile
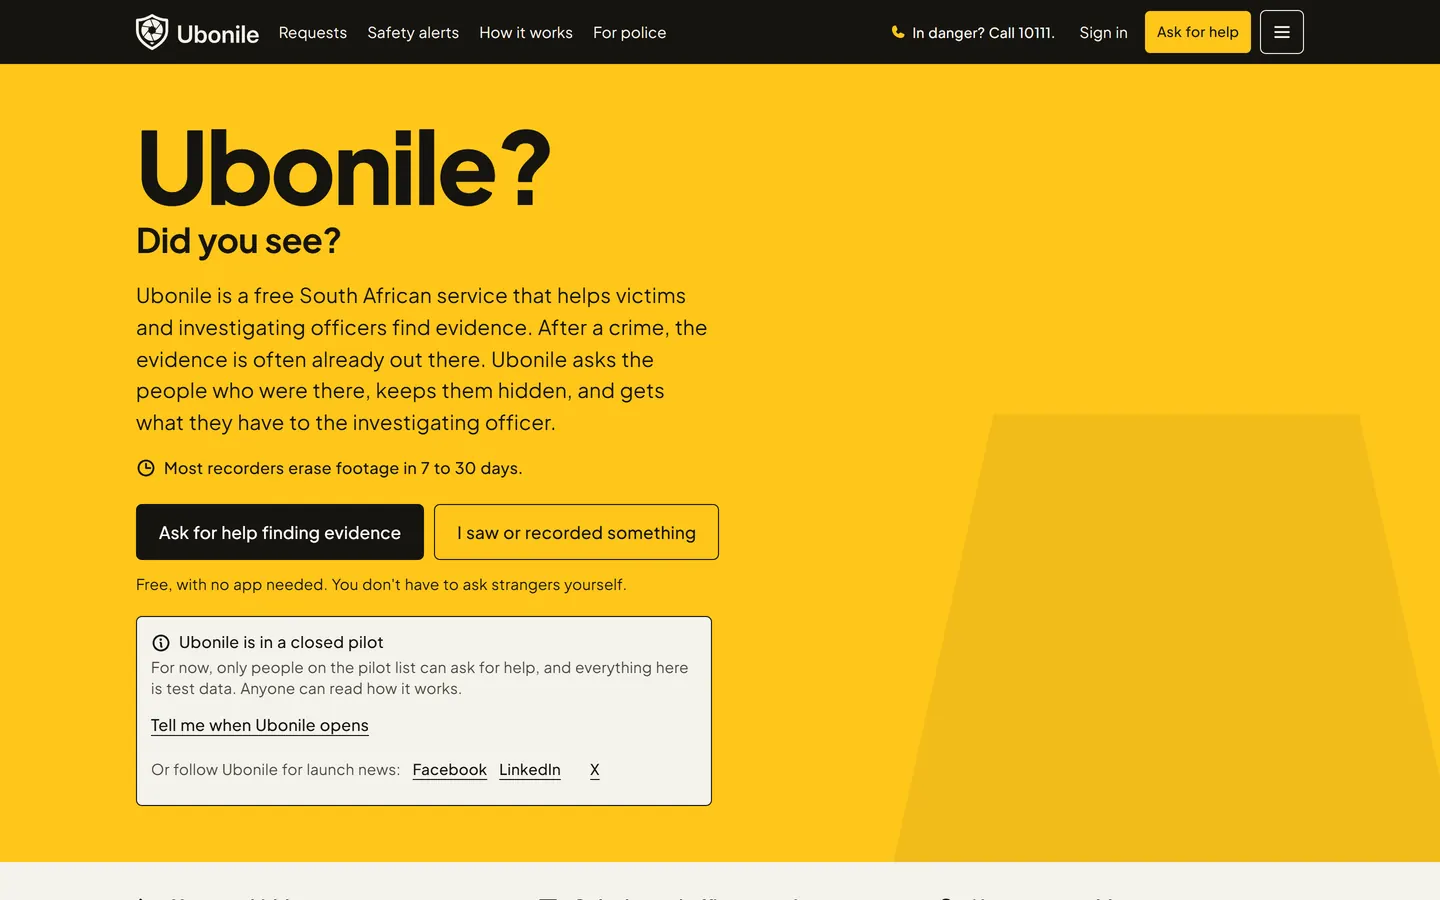
Helps South African communities find witnesses and camera footage after a crime, while keeping the people who answer private.
View project: UbonileCapabilities
Threat modelling, secure coding, dependency management and security tests in the pipeline, as part of the definition of done.
Reviews of web applications and APIs for common weaknesses such as broken access control, injection and exposed secrets.
Least-privilege services, firewalls that actually apply to containers, closed ports, current patches and secure defaults.
Tracking of framework and library advisories, with upgrades planned before they become emergencies.
Containment, investigation, clean rebuilds and a written report, then the fixes that stop it happening again.
Access control, audit trails, encryption and retention settings that support your POPIA security safeguards.
Approach
We treat security as engineering: the same controls are designed, tested, documented and maintained like any other feature. Findings come with clear fixes and priorities, and we explain risks in language a board or an audit committee can act on.
FAQ
A structured review of a web application or API for weaknesses that attackers exploit, such as broken access control, injection flaws, insecure configuration and exposed secrets, followed by prioritised fixes.
Keep frameworks and dependencies patched, run services with least privilege, monitor for unusual activity, test backups and review access regularly. Most serious incidents start with an outdated component or an exposed service.
Yes. Section 19 requires appropriate, reasonable technical and organisational measures to protect personal information, and section 22 requires notification of security compromises.
POPIA and platform securityRelated
Related reading
No learning platform is POPIA compliant on its own. Here is what a POPIA-ready LMS should give you, and the questions to put to any vendor.
Residency, sovereignty and POPIA's cross-border rules explained, with the questions to ask before you decide where a platform is hosted.
Next step
Share the outcome you are responsible for, the people it serves and any deadline or tender reference. We reply with our questions and a proposed next step.
Or email info@ainexim.com